
Getting Started in the ZAP
Manage care team users and patients, and sign in to the Zus App with a password, MFA, or SSO, so your team can start using the ZAP.
Managing users
Zus provisions an initial admin user for each new customer account. That admin can add the rest of their care team.
In the Zus App, go to Admin Settings → Users to view, search, sort, add, edit, or delete users.
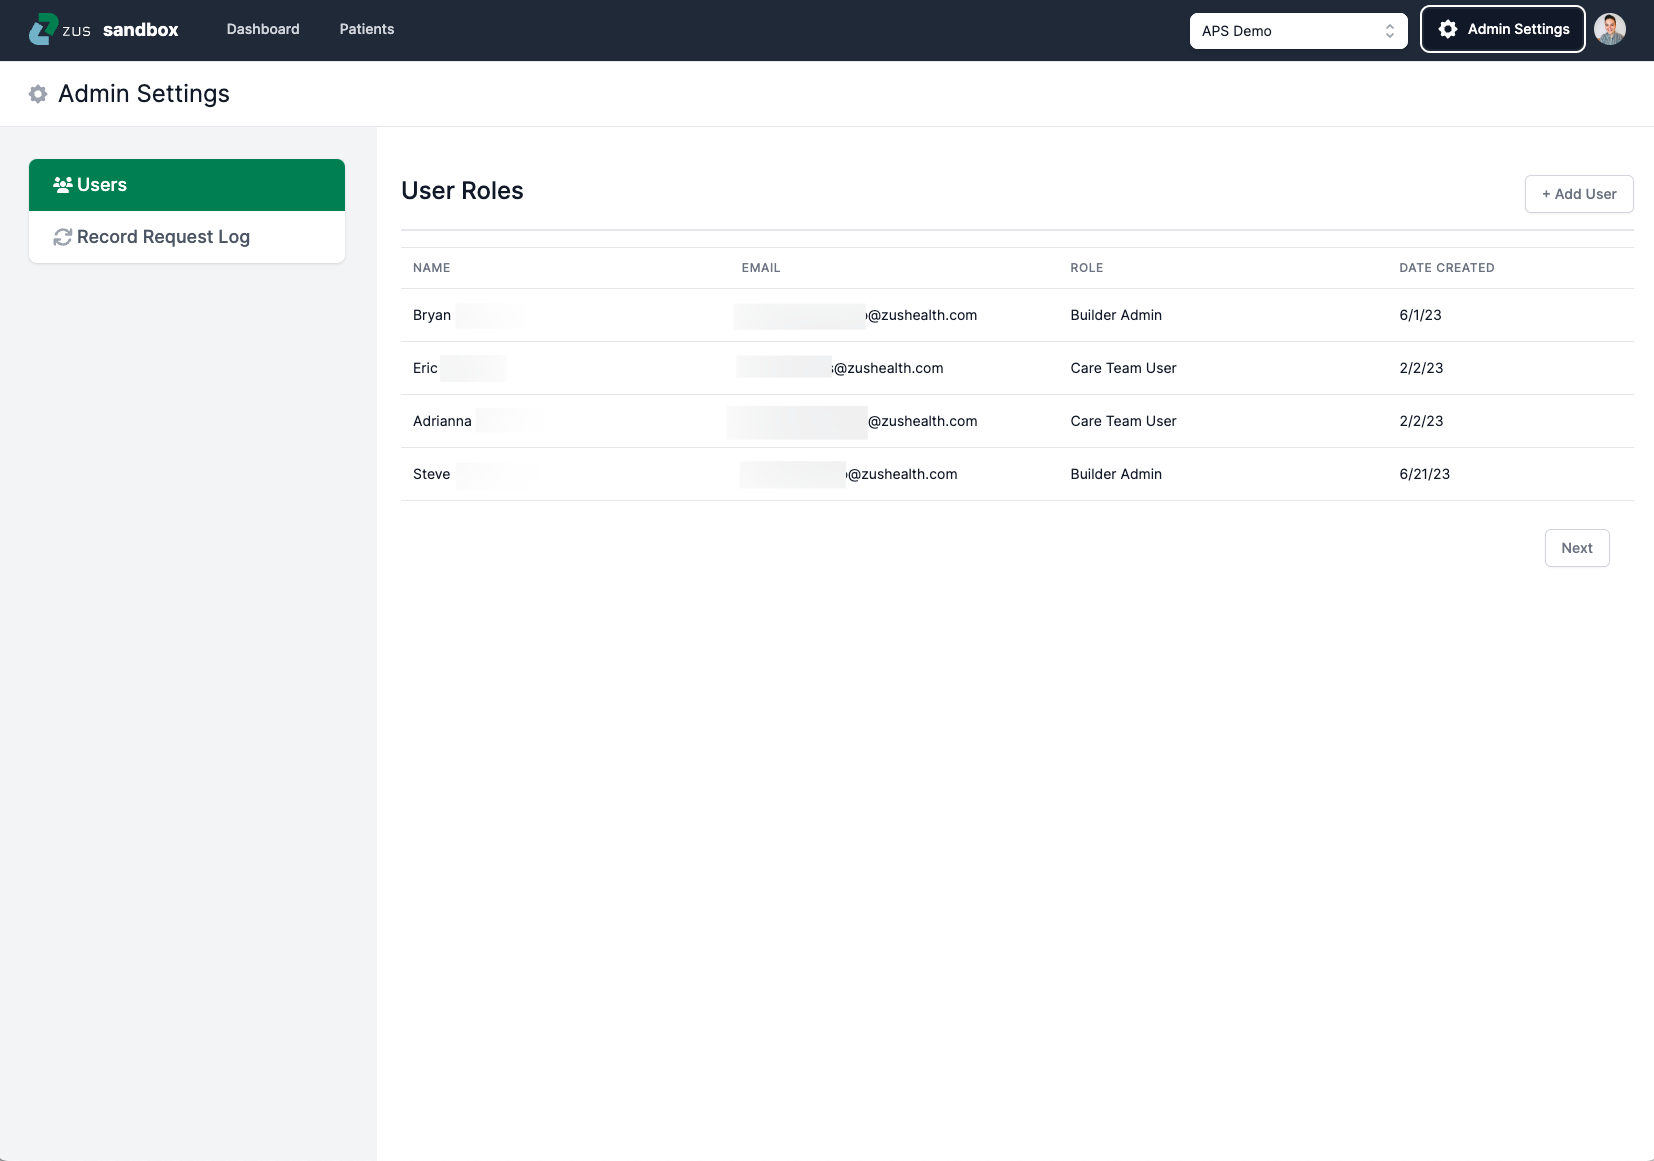
It is important that each user is also linked to a practitioner resource. To automate user provisioning, integrate with your own onboarding flow, or link users to FHIR Practitioner resources at creation, use the Auth Service API instead. For help with your configuration, feel free to reach out to the Zus team.
Signing in to the Zus App
Set your password
When your account is created, you'll receive an email with a password-reset link. Click it to set a password that meets the Zus password policy:
- At least 8 characters
- At least 3 of the following 4 character types:
- Lowercase letters (a–z)
- Uppercase letters (A–Z)
- Numbers (0–9)
- Special characters (e.g.,
!@#$%^&*)
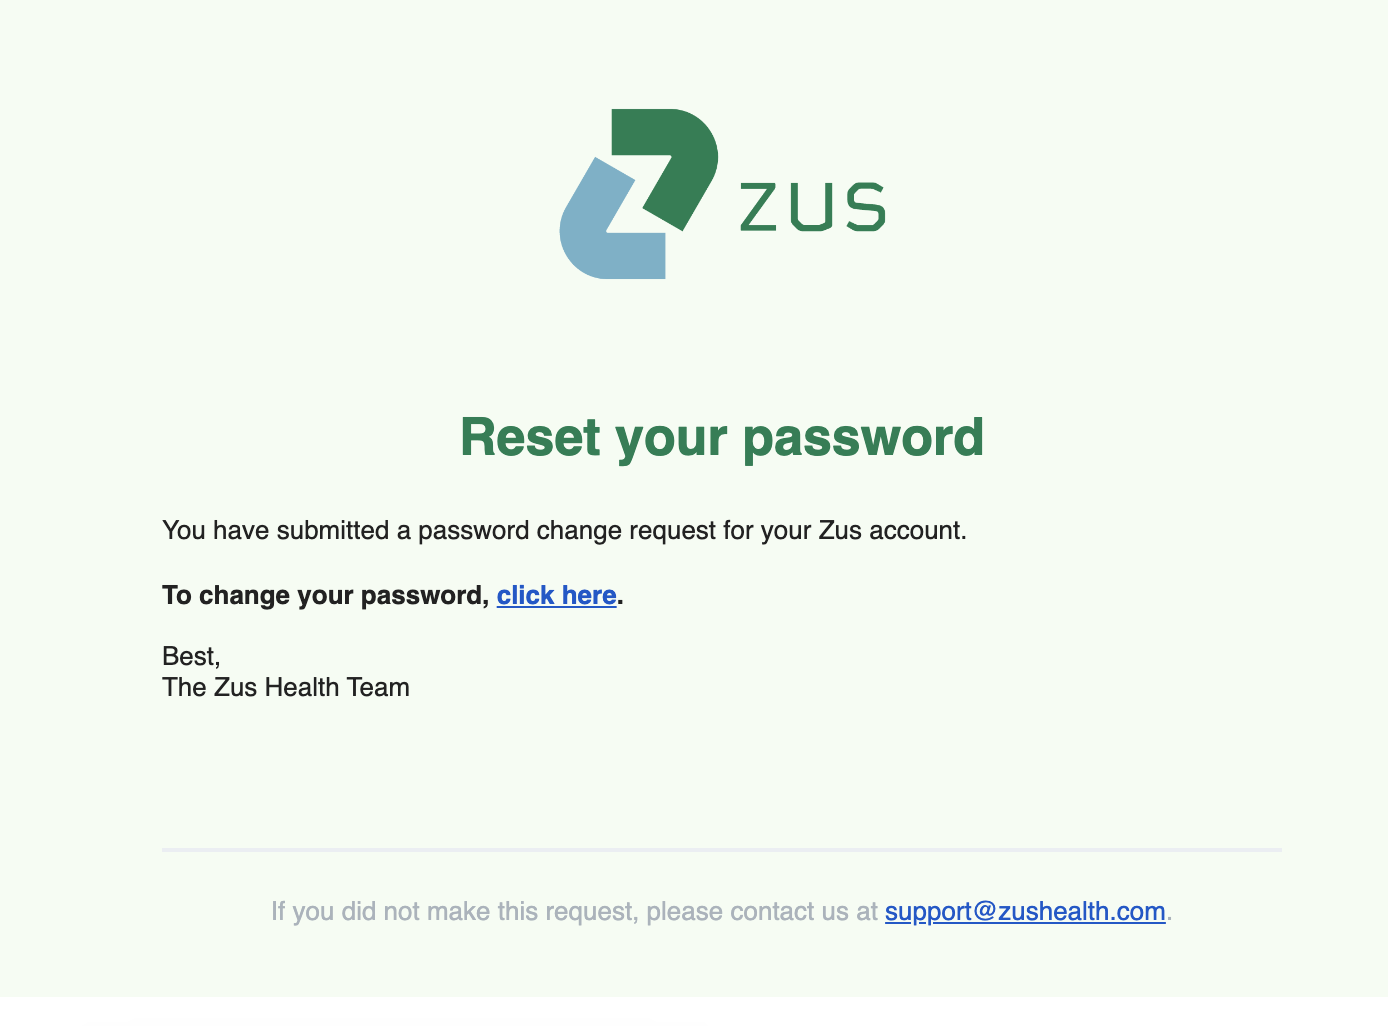
Reset link expired? Go to the Zus App (production or sandbox), enter your email, click Continue, then click Forgot password? to request a new link.
Set up multi-factor authentication (MFA)
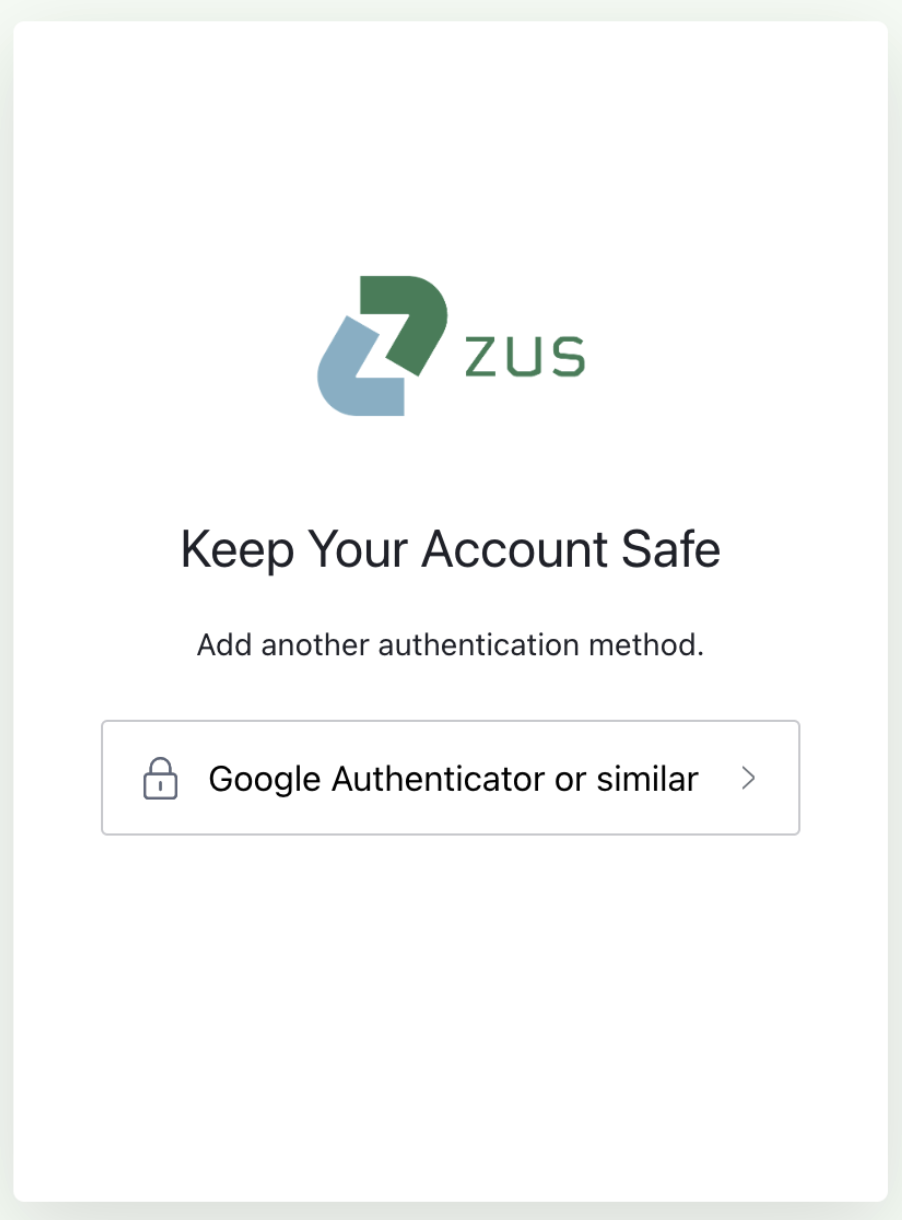
To keep your account secure, MFA is required for all Zus accounts. The first time you log in, you will be prompted to set up MFA using an authenticator app of your choice (Google Authenticator, Authy, 1Password, etc.). You will be prompted to re-verify MFA every 24 hours.
Sign in with SSO
If your organization has configured SSO, you can sign in with your enterprise identity provider instead of a Zus password.
Supported identity providers:
- AWS Cognito
- Google Workspace
- Microsoft Entra ID (formerly Azure AD)
- Okta
Need a different IDP? Submit a support ticket - Zus adds providers based on customer demand.
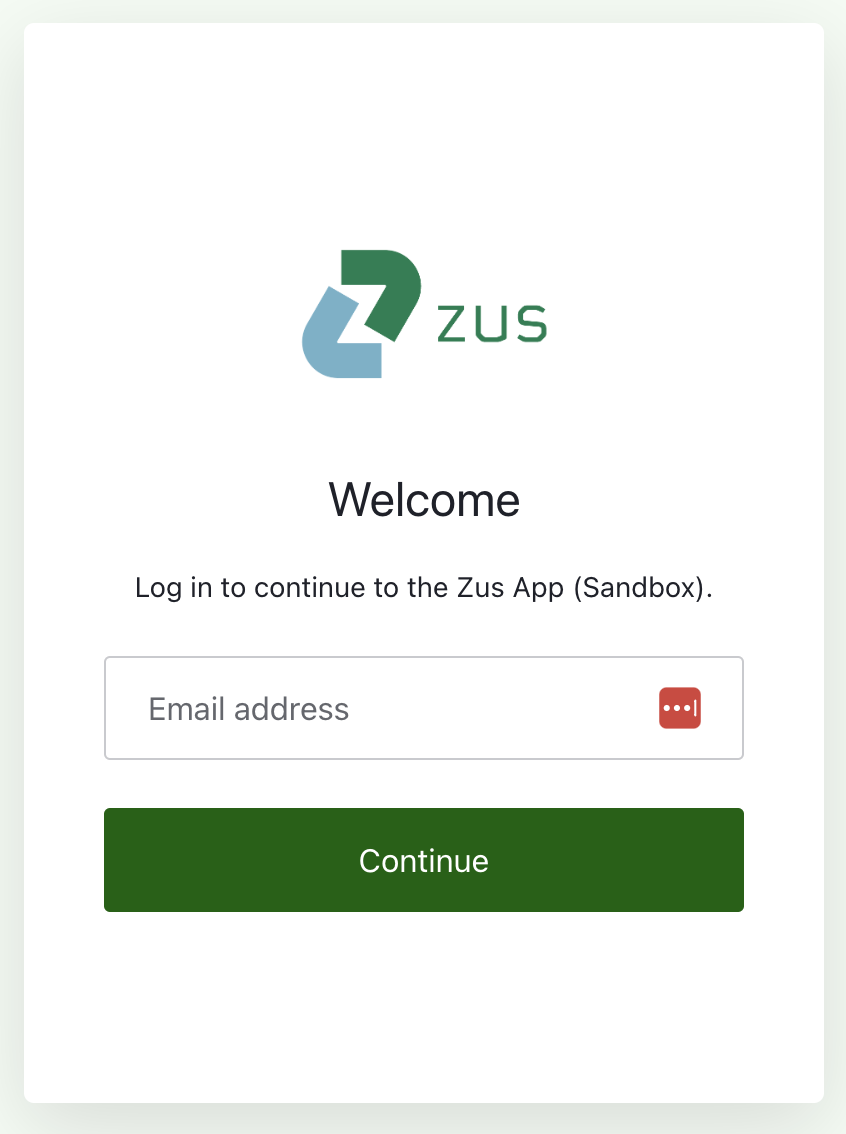
How it works: Enter your email at the login page. If your email domain matches a configured identity provider, Zus redirects you there to authenticate ("home realm discovery"). Otherwise, you'll be prompted for your Zus password.
SSO requirements
- Your IDP must enforce MFA for all users accessing the Zus domain. Customers must attest to this when configuring SSO.
- Zus rotates SSO credentials annually. Customer Success will reach out when it's time to rotate.
To request SSO setup for your organization, submit a support ticket and our team will share a link to an SSO setup guide for your IDP.
Managing patients
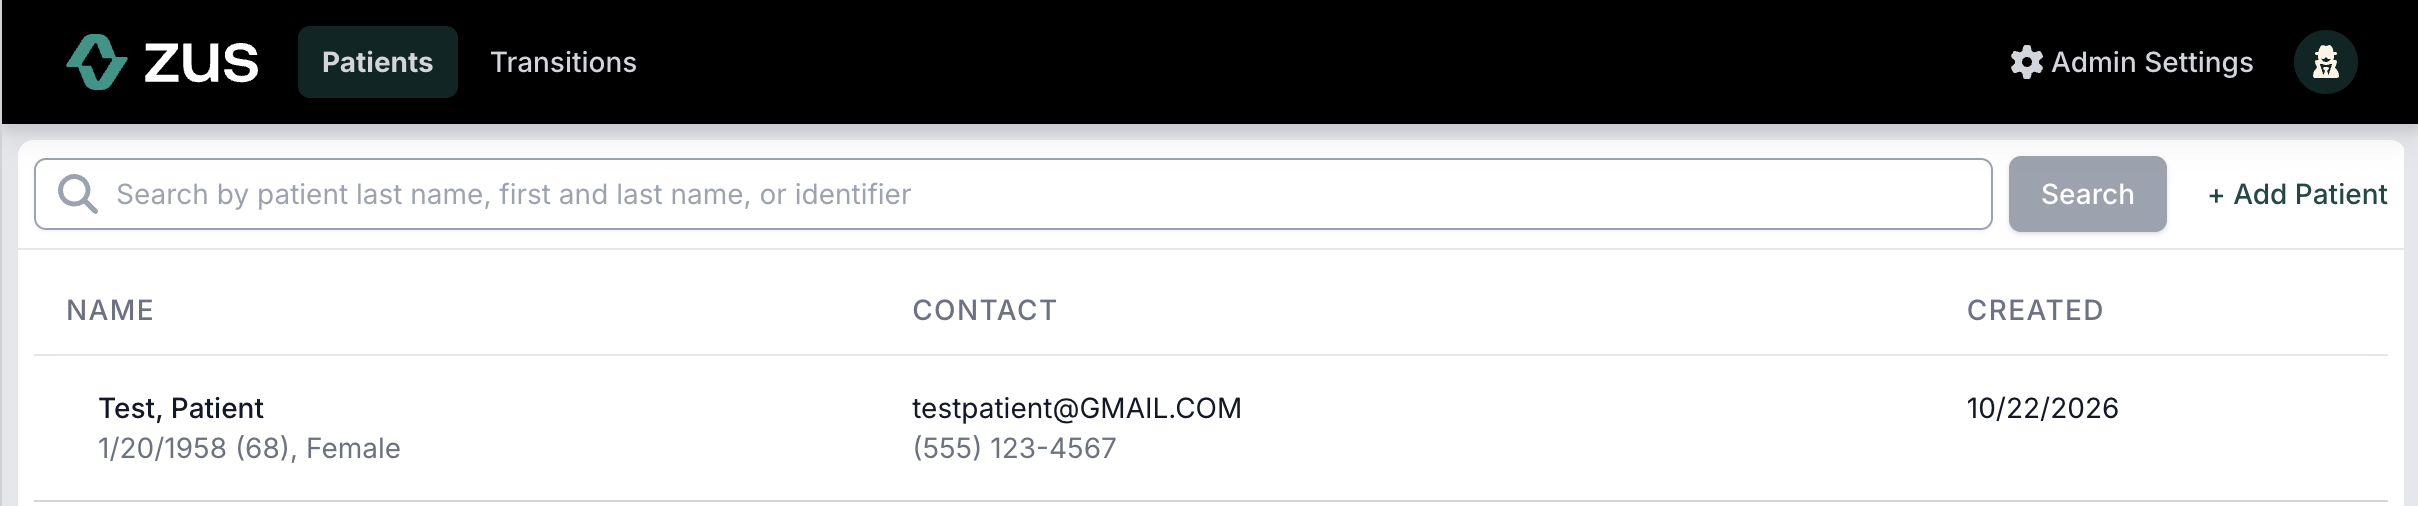
Patients may either be added via API or manually through the user interface. Please take care to ensure key demographics and contact information are included, as this greatly increases our ability to match patient history in partner networks. The other alternative is for clinical users to manually add patients via the user interface using the “Add Patient” button.
Updated 6 days ago